
Your account
Notifications & Profile
Keep personal account details current, control notification noise and understand the security context of your active session.
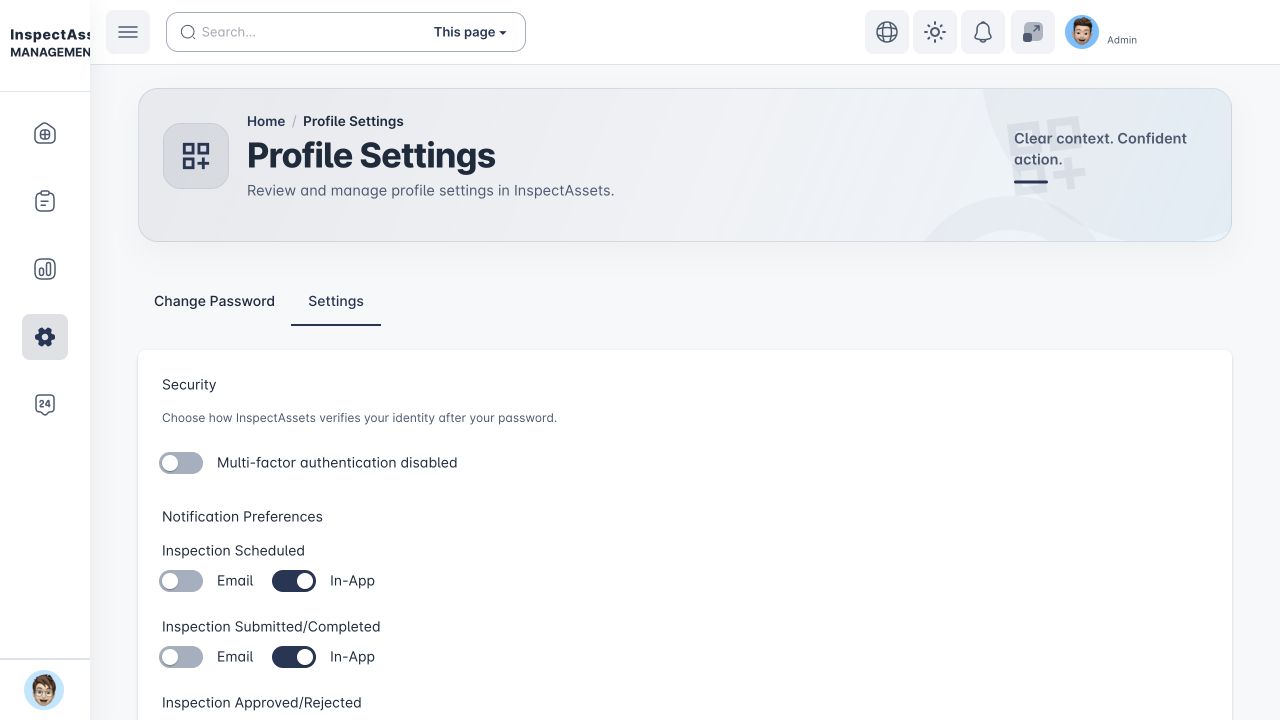
Notifications
The Notifications area shows your in-app messages and unread/total counts. Notification Preferences control which supported events reach you through available channels such as email versus in-app notification.
Choose preferences around your responsibility. An inspector may need assignment and field-work updates; a manager may care more about approval, overdue or exception events. Turning everything on can make urgent signals harder to notice.
Profile Settings
Use Edit Profile to keep your name and contact details accurate. Correct identity data matters because inspection, approval, limitation and audit records should be attributable to a real person rather than an ambiguous account.
Depending on your account configuration, the profile/security area can also expose password and MFA controls plus a summary of your current role/permissions.
Password and MFA
Change a local password when required by policy or after an administrator reset. In Settings → Security, MFA can use either a verification code sent to your verified email or a TOTP-compatible authenticator app such as Google Authenticator or Microsoft Authenticator.
- Email MFA: a fresh 6-digit code is sent to your registered email when verification is required.
- Authenticator app: scan the setup QR code, confirm the current 6-digit app code, and save the recovery codes shown after setup.
- Changing methods: verify your identity before switching between email and an authenticator app. Existing authenticator secrets and recovery codes are revoked when you switch away from the app.
- Recovery codes: each code works once. Store them outside the device that holds your authenticator app and regenerate them if their confidentiality is uncertain.
Lost authenticator device
Try a saved recovery code first. If you cannot access the authenticator or recovery codes, contact support. An authorised Platform Support Manager or Global Admin can start an audited MFA recovery from a linked support ticket, with recovery delivered only through your already-verified email address. If you have also lost access to that email address, the automatic recovery path is not available.
Impersonation sessions
Acting as another user
If a banner says you are currently acting as another user, you are in an administrative impersonation/support session. Actions remain attributable to that controlled context and can be audited. Exit impersonation as soon as the support task is complete.