
Traceability
Audit Logs
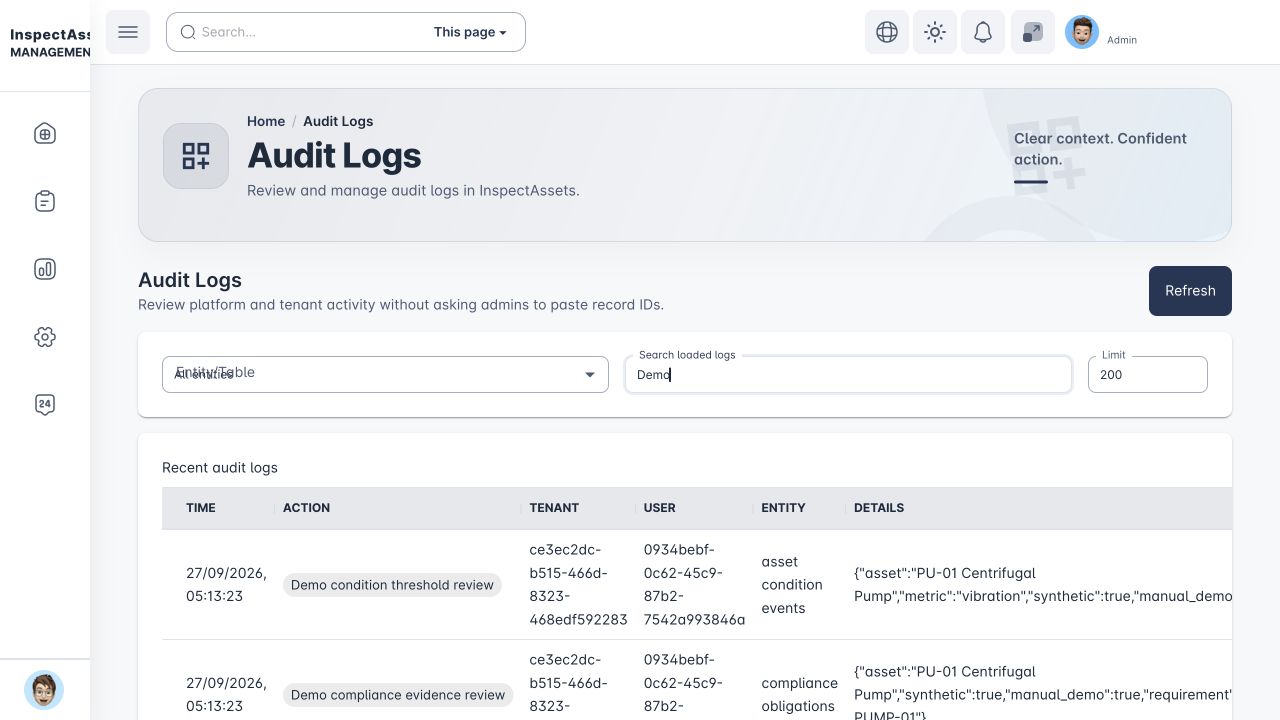
Review the history of material actions across the platform and answer who changed what, when and in which tenant context.
Requires: audit_logs or manage_tenants
The audit log is evidence of system activity
Use it when the decision depends on change history: role/permission changes, administrative configuration, approval actions, tenant operations and other audited events. It complements the inspection evidence record; it does not replace it.
What to use it for
- Investigating an unexpected access or configuration change.
- Confirming when a material action was performed and by whom.
- Supporting an internal or external control review.
- Tracing platform-admin or impersonation activity where recorded.
- Checking approval/uncertainty decision history alongside the inspection record.
Filtering
Use available date, user, tenant/action and other filters to narrow the event set. If the log appears empty, clear or widen filters before assuming no audit activity exists.
Audit logs vs business evidence
An audit event can show that someone changed or approved something. The inspection, evidence passport, corrective action or compliance record contains the domain evidence explaining the underlying condition. For a defensible review, use both where appropriate.
Exports
Audit-log export availability can depend on permissions and subscription entitlement. Keep exported logs inside your organisation's approved evidence-retention process and avoid sending a broad event export when a narrower evidence portal or report would answer the external review.